IT compliance management
Practical IT compliance, without compromise.
Operational IT compliance software that makes it easy to run audits, track alignment, and maintain standards continuously, not just at audit time.
Month to month. Unlimited users. 30-day money-back guarantee, no questions asked.
For managed service providers
Run the same standard across every client, and walk into a quarterly review with evidence instead of adjectives.
How MSPs use Spectra Core →For credit unions and small financial institutions
Produce the technology risk evidence your regulator, auditor or board is asking for, on a schedule you can defend.
How financial institutions use it →Curated Standards
Start with a library of controls informed by industry frameworks like CIS and NIST CSF.
Build Your Own
Adapt standards or create entirely custom programs that fit your organization.
Measurable Risk Reduction
Every control you adopt drives real, quantifiable reduction in risk. No checkbox theatre.
Streamlined Evidence
Gather and organize evidence in one place. No more chasing screenshots and spreadsheets.
Instant Reporting
Generate polished, audit-ready reports in minutes and cut compliance cycles from weeks to days.
Onboarding Assistance
Our team helps you get set up and running, with guidance and support from day one.
No Limits
Unlimited audits, standards, and users. Scale your compliance program without restrictions.
Month-to-Month Terms
No long-term contracts. Stay because it works, cancel any time.
Not a GRC Tool
Pull the most useful controls from industry frameworks and turn them into practical, ongoing compliance programs.
Workflow
How it works
A structured workflow for planning, executing and reporting on IT audits, built for internal IT teams and managed service providers alike.
- 01
Set up your audit
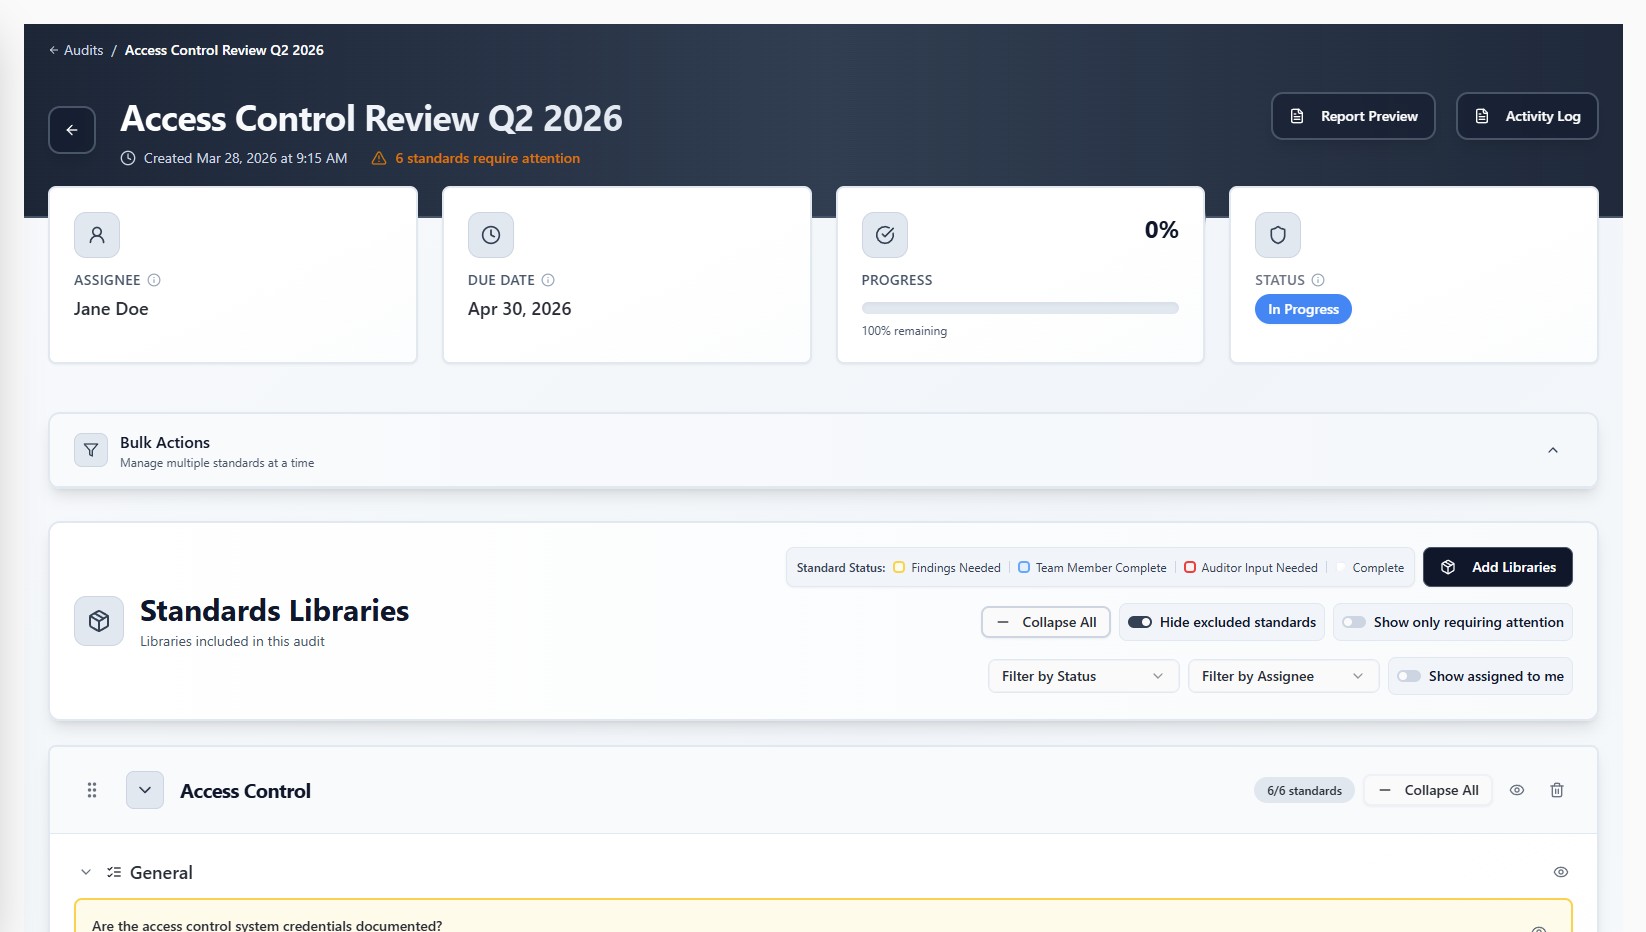
Create a new audit from scratch or reuse the structure of a previous one. Select from existing standards libraries or build your own, exclude anything that is not relevant, and tailor the scope to exactly what needs reviewing.
- 02
Execute the audit
Engineers are assigned standards based on expertise, submit findings with supporting evidence, and collaborate inside each standard. For smaller teams, one IT generalist can carry the whole audit.
- 03
Review and report
The audit owner reviews findings and sets risk levels. AI-generated executive summaries produce structured, customisable reports, shared securely with interactive filters and print support.
Standards
Core libraries included
Get started instantly with curated libraries covering the most common IT standards. Need something specific? Create your own to match your environment, or your clients' expectations if you are an MSP.
Remote Monitoring & Management
Alerting, patching, agent health, and endpoint visibility standards
Network Environment
Switching, routing, Wi-Fi, DNS, and network segmentation checks
Active Directory Configuration
GPOs, OU structure, password policies, and domain hygiene
Network Security
Identity, access management, and endpoint protection / EDR standards
Microsoft 365 Security
Identity threat detection and response, conditional access, and tenant hardening
Backup & Disaster Recovery
On-premise DR systems and Microsoft 365 backup configuration checks
Server Rooms
Physical environment, cooling, fire suppression, and monitoring standards
Racks
Cable management, labeling, power distribution, and physical organization
Service Management
Ticketing workflows, SLA tracking, escalation, and change management
Power Management
UPS health, generator readiness, redundancy, and power monitoring
Access Control
Physical and logical access policies, badge systems, and visitor management
Cost Control
Licensing optimization, vendor spend, and budget alignment checks
Documentation
Network diagrams, runbooks, SOPs, and asset inventory standards
Customer Service & Client Confidence
Client reporting, QBR readiness, and SLA transparency (MSPs)
See it against your own environment
Twenty minutes, your systems, no slides. We will build the first audit with you on the call.